CompTIA CySA+ Blue Team Guide: Threat Hunting, Log Analysis & Incident Response
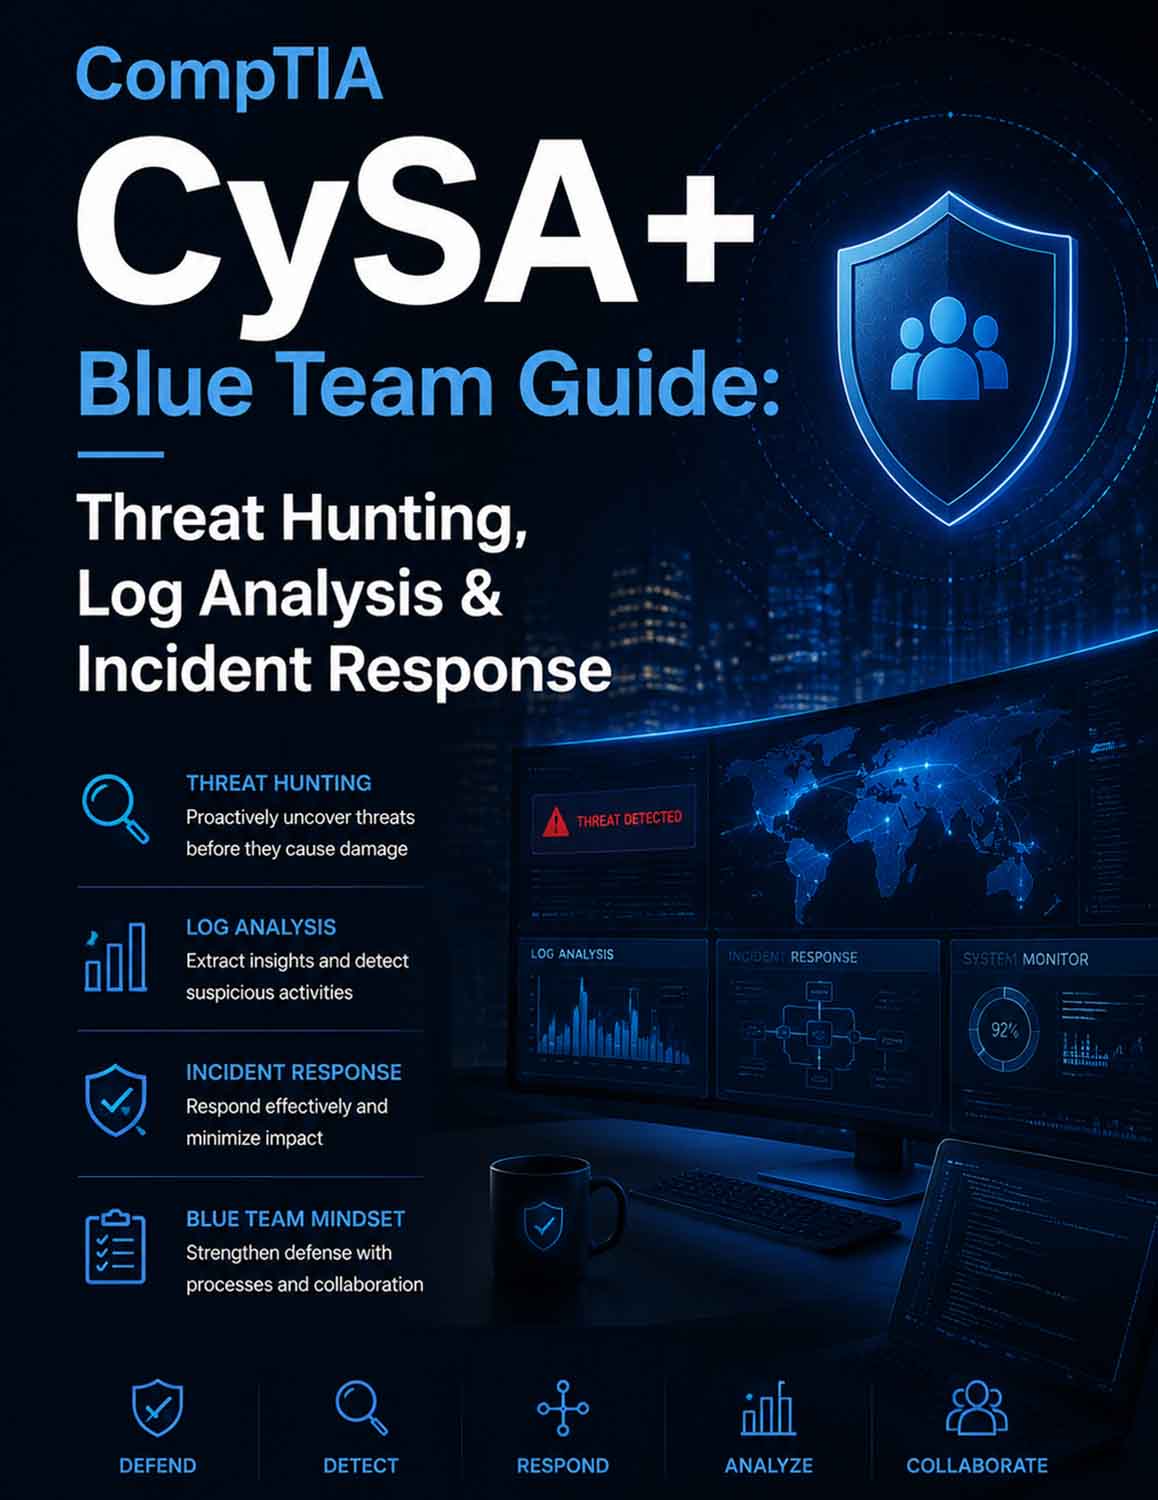
Built for aspiring SOC analysts and defense-focused professionals, this guide bridges the gap between theoretical knowledge and hands-on threat detection. It delves into the daily routines of a cybersecurity analyst, demonstrating how to parse SIEM logs, analyze vulnerability scan outputs, and leverage the MITRE ATT&CK framework for effective threat hunting. By walking readers through standard NIST incident response lifecycles and real-world IoC identification, this book prepares candidates to think like seasoned defenders on the CySA+ exam.
主题授权提示:请在后台主题设置-主题授权-激活主题的正版授权,授权购买:RiTheme官网
Notice: Unless explicitly stated otherwise, all content on this website is original. Unauthorized copying, scraping, aggregating, or republishing of our material across any media platforms (including websites, publications, and social media) is strictly prohibited without prior written consent. If you believe any material on this site infringes upon your copyright, please contact us immediately for prompt removal or resolution.
